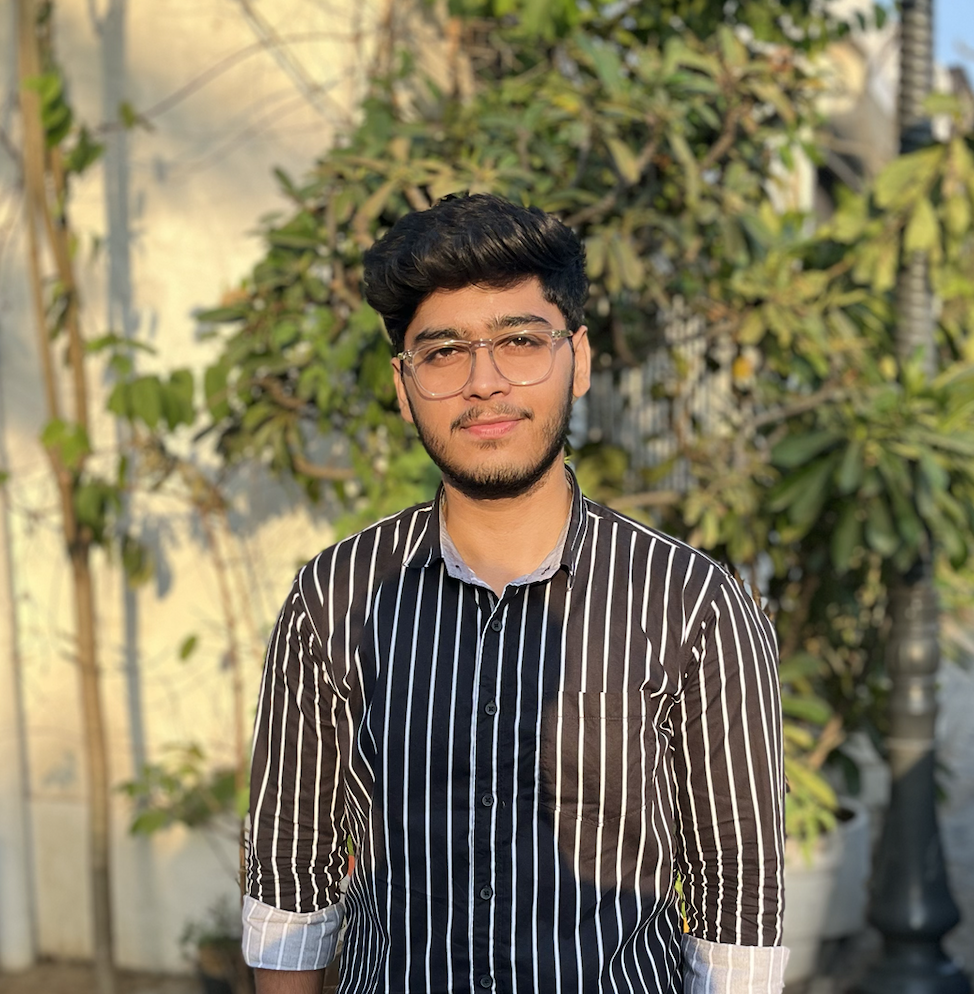
NEW DELHI, INDIAAVAILABLE FOR THE RIGHT PROBLEM

SECURITY ENGINEER / 01

Digvijay
Singh.

Digvijay Singh

I investigate what a system is doing, why a control reacts, and where the real risk is hiding.

API SECURITY · BAS · VAPT · ZERO TRUSTEXPLORE THE RECORD ↓

01 / COMMUNITY & TALKS

MLSA · GDG · SECURITY EDUCATION

Learning in public.
Teaching in practice.

Workshop sessions, CTFs, and the moments that turned study into something shared.

SELECTED RECORD / 01

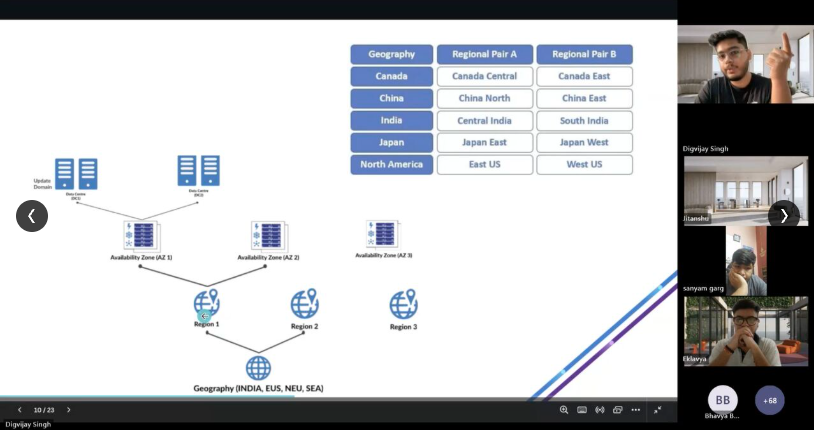
Azure Fundamentals, from first principles to secure access.

Hosted as a Microsoft Learn Student Ambassador. Covered cloud basics, deployment models, Azure core services, Azure Active Directory, and ended with an interactive quiz.

Open source ↗
02 / EXPERIENCE

SELECT A POINT ON THE TIMELINE

The work behind
the point of view.

Three roles, one growing practice: moving from testing systems to protecting and validating them in production.

Resident engineering for enterprise security programmes, working at the meeting point of application teams, security controls, operational investigations, and stakeholder decisions.

WHAT I DID

  • Owned day-to-day API security engineering: discovery and inventory work across applications and API gateways, including the identification of shadow and zombie APIs that need scrutiny.
  • Turned API traffic into a clearer risk picture by carrying out posture assessment and sensitive-data classification across request and response payloads, then translating findings into management-ready reporting.
  • Configured and tuned positive security models, WAF rules, rate limits, bot classification, and access policies while investigating security events and separating false positives from meaningful signals.
  • Coordinated the operational work surrounding security changes—policy migration, traffic-diversion dependencies, validation, troubleshooting, and the impact on legitimate application behaviour.
  • Delivered 5+ Picus Security POCs and deployments, validating detection and prevention coverage across EDR, firewall, WAF, email security, and DLP controls.

KEY LEARNING

Strong security engineering is not just about deploying a product. It is about tracing dependencies, reading real traffic, making a defensible decision, and leaving the system more reliable than it was before.

TOOLS & TECHNOLOGIES

Radware API SecurityCloud WAFPicus SecurityZscalerNetskope

03 / CREDENTIALS

VERIFIABLE RECORDS

Proof of
continued practice.

Each credential links to its verification record where one is available.

04 / DEEPER WORK

CASE STUDIES / IN DEVELOPMENT

Once you know the
journey, look closer.

05 / RECOMMENDATIONS

THREE PEOPLE, THREE PERSPECTIVES

How the work
lands with people.

“He moved from power user to a key member of the tech team—taking ownership of QA, regression automation, penetration testing, user support, and requirements.”

“His detail orientation ensures no stone is left unturned. He is proactive, adaptable, reflective, and a teammate who uplifts the people around him.”

“He combines creative problem-solving with initiative, startup-minded openness, and a serious commitment to making cybersecurity work matter in practice.”